Both approaches create separate browsing contexts, but they are designed for different scales. Rather than publishing unverifiable competitor numbers, this comparison offers a criterion-by-criterion framework you can confirm against official documentation and your own trial.
Why profile approach comparison matters for multi-account teams
The phrase chrome profiles vs multi session browser is slightly misleading, because the two are not direct substitutes at the same scale. A conventional browser profile is a lightweight way for one person to keep a few contexts apart. A multi session browser is a workspace built so that many accounts, several teammates and a set of network routes can be managed as one system. The right question is therefore not which one is better in the abstract, but at what point the lighter option stops being adequate.
Ask an experienced operator what a messy morning looks like and the answer is rarely strategy. It is switching between logins, confirming that the right session is attached to the right account, and re-checking work somebody else already did. A clear approach to profile approach comparison is what turns those repeated checks into a short, boring, repeatable routine for teams evaluating their tooling.
There is also a people dimension. When only one laptop holds the working context, a holiday, a hardware replacement or a new teammate can stall the whole operation. Cloud account sync and role-based permissions address the people side, while isolated sessions address the technical side. Both are needed before comparing standard browser profiles with a multi session browser can be considered done.
- One isolated profile per account, with separate cookies, cache, local storage and bookmarks.
- One recorded proxy route per profile, reviewed whenever the account's region changes.
- Role-based permissions that match what each teammate actually does.
- Cloud sync so the workspace does not depend on a single laptop.
- Batch launch to remove repetitive opening and closing of profiles.
- A written owner for every account and a short handover note.
A short definition
For this guide, profile approach comparison means the documented set of conventions that keep browsing state, network routes and human permissions attached to the right account. It is a process, not a single setting.
Defining it this way makes the rest of the article testable: each section below describes something you can check in a workspace rather than a claim you have to take on trust.
- One isolated profile per account, with separate cookies, cache, local storage and bookmarks.
- One recorded proxy route per profile, reviewed whenever the account's region changes.
- Role-based permissions that match what each teammate actually does.
How comparing standard browser profiles with a multi session browser works in a Chromium-based workspace
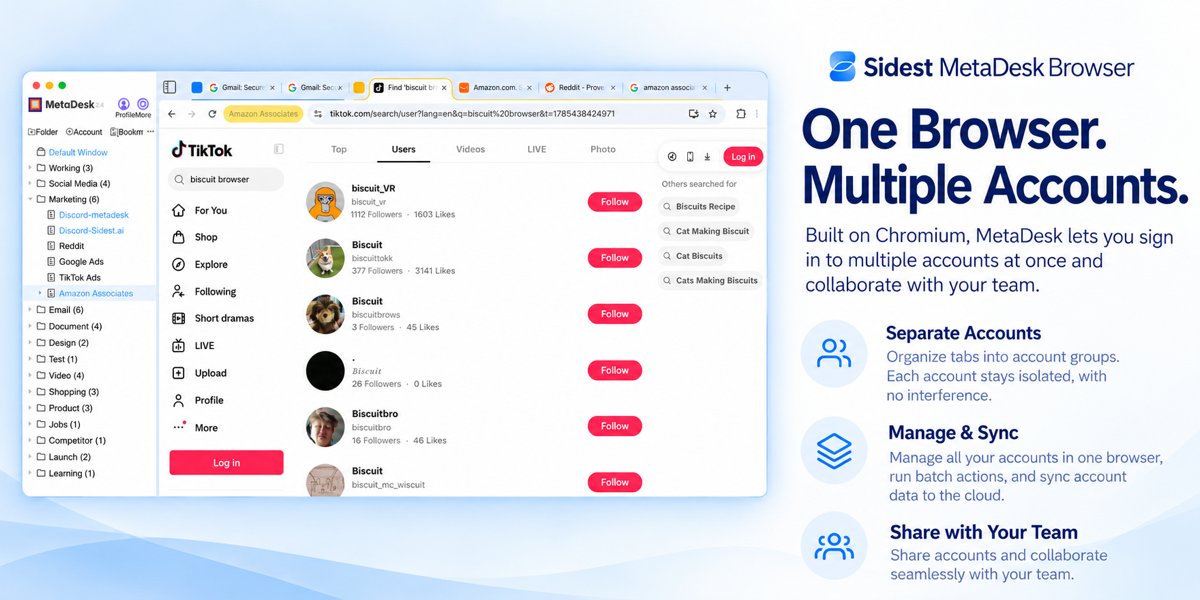
We deliberately do not publish competitor specifications, benchmark numbers or pricing claims we cannot verify. Instead, the table below lists criteria and tells you where to confirm them: official product documentation for a given tool, and your own trial for anything about your workflow. MetaDesk is described only against the product facts available publicly: isolated sessions with separate cookies, cache, local storage and bookmarks, cloud sync, team roles, batch launch, per-profile proxy settings, ad campaign management, bookmark management, Windows and macOS clients, and free registration.
It helps to describe what isolation is not. It is not simply a second window, and it is not a private tab that forgets everything on close. It is persistent, separate storage per account that survives restarts and can be handed to a colleague. That persistence is exactly why comparing standard browser profiles with a multi session browser needs a naming and ownership policy.
The network layer is separate again. Assigning one proxy route per profile keeps the connection consistent with the region an account belongs to, and documenting the mapping prevents the most common configuration drift. Add ad campaign grouping and bookmark sets on top, and profile approach comparison becomes a system an agency can explain to a new hire in one sitting.
- Chromium rendering keeps pages familiar for new teammates.
- Isolation covers persistent state, not just separate windows or tabs.
- Bookmark management keeps each account's shortcuts in the right profile.
- Ad campaign grouping organises logins by client or brand.
- Windows and macOS clients share the same workspace model.
Why the profile is the right unit
Profiles are the smallest thing that can hold session state, a bookmark set, a proxy route and a permission at the same time. Making them the unit of configuration keeps profile approach comparison understandable for a new teammate.
Group profiles by client or brand for batch work, but keep the individual profile as the place where settings live. Grouping is for convenience; isolation is per profile.
- Chromium rendering keeps pages familiar for new teammates.
- Isolation covers persistent state, not just separate windows or tabs.
- Bookmark management keeps each account's shortcuts in the right profile.
How to evaluate options for profile approach comparison
A fair comparison starts with criteria and ends with evidence. Decide what must be true for your workflow, then confirm each point against official documentation or a short trial. This order matters: starting from a brand shortlist tends to turn the evaluation into a search for reasons to justify a decision already made.
We do not publish unverified competitor specifications, benchmark numbers or prices. Feature lists change and copied figures age badly. The table below is a framework you can fill yourself, with a source column so every score has an attributable answer.
- Weight criteria before looking at any product.
- Confirm plan limits and prices only on official pages, with the date noted.
- Use the same two-account trial script for every candidate.
- Separate observed behaviour from documented claims.
- Do not copy competitor specifications you cannot verify.
| Criterion | What to verify | Where to confirm |
|---|---|---|
| Session isolation | Cookies, cache, local storage and bookmarks are separate per profile | Two-account trial and official docs |
| Cloud sync | Profiles and settings appear unchanged on a second device | Handover test on another machine |
| Roles and permissions | Launch, edit and export rights can be granted separately | Official docs plus a colleague in the trial |
| Batch management | A group of profiles can be launched and updated together | Timed batch-launch test |
| Per-profile proxy | Each profile keeps its own recorded network route | Configuration screen and mapping table |
| Platform support | Windows and macOS clients share the workspace model | Official download and version notes |
| Export and recovery | A profile export can be restored after a device change | Scheduled restore test |
| Commercial terms | Current plans, limits and prices | Official pricing page, with the date checked |
Keeping the review honest
Write the source next to every score. 'Observed in trial', 'confirmed on official documentation on this date' and 'unverified' are three very different answers, and conflating them is how a comparison quietly becomes marketing.
If a candidate cannot be tested for a criterion, leave the row blank rather than filling it with an assumption. A blank row is a useful to-do; a guessed score is a future correction.
- Weight criteria before looking at any product.
- Confirm plan limits and prices only on official pages, with the date noted.
- Use the same two-account trial script for every candidate.
Common mistakes with comparing standard browser profiles with a multi session browser and how to fix them
A useful way to audit an existing workspace is to look for decisions that live only in somebody's head. If the reason a profile is named a certain way, or why a route was chosen, cannot be recovered from a document, that decision is a liability.
Work through the table and mark each row as done, open or not applicable. Two open rows are normal during a first review; two open rows six months later are a process problem, and profile approach comparison will not improve until they are closed.
- Fix the template, not just the single profile that failed.
- Record why an exception exists and when it should be reviewed.
- Re-test isolation after any client update or device change.
- Keep the review short enough that it actually happens weekly.
| Mistake | Why it hurts | Fix |
|---|---|---|
| Reusing one profile for several accounts | Shared cookies and local storage make sessions ambiguous | One isolated profile per account |
| Choosing proxy routes from memory | Two operators pick different routes for the same account | Record the mapping in the access policy |
| Leaving permissions wide open | Access survives role changes and offboarding | Least privilege plus a monthly review |
| Naming profiles after people | Names stop making sense after a reorg | Name after client, brand, platform and role |
| Treating sync as a backup | A sync error has no point-in-time recovery | Schedule exports and test a restore |
Turning fixes into defaults
Whenever you correct a profile, ask what would have prevented the mistake. Usually the answer is a template, a required field in the naming convention or a step in the handover checklist.
Update the default and note the change in the access policy. That is how a one-off cleanup becomes a lasting improvement to comparing standard browser profiles with a multi session browser.
- Fix the template, not just the single profile that failed.
- Record why an exception exists and when it should be reviewed.
- Re-test isolation after any client update or device change.
Metrics that show whether profile approach comparison is working
Avoid vanity measures such as the total number of profiles created. Volume grows naturally with the business and says nothing about quality. Prefer rates: how many profiles have a recorded owner, how many mappings were reviewed this month, how many handovers needed help.
Review the results with the people doing the work. If a metric looks good but operators still keep a private spreadsheet of workarounds, the spreadsheet is the more accurate signal about comparing standard browser profiles with a multi session browser.
- Measure a baseline before changing anything.
- Prefer rates and times over raw counts.
- Ask operators what still feels confusing each week.
- Repeat the same measurement two weeks after rollout.
| Metric | What to compare | How to collect |
|---|---|---|
| Time to first correct launch | New teammate before vs after rollout | Stopwatch during onboarding |
| Profiles with a recorded owner | Percentage of total profiles | Monthly workspace review |
| Mapping reviews completed | Percentage of routes reviewed this month | Mapping table with dates |
| Handovers needing help | Count per week | Short weekly team note |
| Recovery time | Minutes to restore a profile from export | Scheduled restore test |
What a good baseline looks like
A baseline does not need to be precise. Time one onboarding session, count how many profiles have a recorded owner, and note how many handovers needed help last week. Three rough numbers are enough to show whether the change helped.
Keep the same definitions at the follow-up. If you change what counts as a handover between measurements, the comparison tells you nothing about profile approach comparison.
- Measure a baseline before changing anything.
- Prefer rates and times over raw counts.
- Ask operators what still feels confusing each week.
When to change the process
If two weeks of measurement show no improvement, look at the step people skip rather than the tool. In most teams that is the ownership record or the proxy mapping, and both are documentation problems with documentation fixes.
Change one thing at a time and measure again. Stacking several process changes at once makes the next result impossible to interpret.
- Measure a baseline before changing anything.
- Prefer rates and times over raw counts.
- Ask operators what still feels confusing each week.
Team roles, permissions and handover
A workspace is a shared resource, so it needs shared rules. Define who can open a profile, who can edit it, who can export it, and who reviews those rights. Least privilege is not distrust; it is simply a way to keep an honest answer to 'who had access' when the team changes.
Write the joiner and leaver steps down. Onboarding is where conventions are learned, and offboarding is where forgotten access is discovered. Both are part of profile approach comparison even though neither appears in a feature list.
- Keep the number of roles small enough to explain from memory.
- Give operators launch rights and owners edit and export rights.
- Review exceptions quarterly with an owner, a reason and an expiry.
- Remove dormant accounts during the monthly review, not later.
- List the work, not the peopleWrite down the tasks people perform: launch, edit, export, review. Roles should map to these tasks.
- Define three or four rolesKeep the set small. Operators, owners and administrators cover most agency workflows without extra complexity.
- Apply least privilegeGrant launch rights to operators and reserve edit and export rights for account owners and administrators.
- Document joiner and leaver stepsWrite the exact actions for adding a teammate, changing a role and removing access, including who approves them.
- Review monthlySpend ten minutes checking that permissions still match the current team and remove dormant accounts in the same pass.
Offboarding without surprises
Removal should be a checklist, not a reaction. Revoke workspace access, reassign profile ownership, rotate anything held outside the browser, and confirm the leaver's exceptions are closed.
Record who performed each step and when. That record is what makes profile approach comparison auditable when someone later asks who had access to an account.
- Keep the number of roles small enough to explain from memory.
- Give operators launch rights and owners edit and export rights.
- Review exceptions quarterly with an owner, a reason and an expiry.
Pre-scale checklist for profile approach comparison
Scaling exposes whatever was informal. A convention that worked for eight profiles usually survives on memory; the same convention across eighty profiles needs to be written down and checked. Use the list below as a gate before adding the next batch of accounts.
If a row fails, fix it before continuing. The cost of pausing a rollout for an hour is small compared with unpicking a naming or permission mistake across a full workspace.
- Every profile has a name following the documented convention.
- Every profile has a recorded owner and second-factor holder in your policy.
- Every profile has one proxy route, and the mapping has been reviewed this month.
- Roles follow least privilege, with exceptions recorded and dated.
- Cloud sync is enabled and a scheduled export has been restored once.
- Isolation was verified with two profiles launched together.
- A joiner and leaver checklist exists and has been used at least once.
| Check | What good looks like | Owner |
|---|---|---|
| Naming convention | Every profile follows client-brand-platform-role | Workspace admin |
| Proxy mapping | One route per profile, reviewed this month | Account owner |
| Permissions | Least privilege, exceptions dated and owned | Team lead |
| Sync and export | Sync on, export scheduled, restore tested | Workspace admin |
| Isolation | Two-profile launch shows no shared state | Operator |
Making the review stick
Put the checklist in the same place as the access policy and give it a recurring owner. A checklist that depends on someone remembering to open it will be opened twice.
Keep failed rows visible until they are fixed. Hiding them makes the review feel complete while the underlying profile approach comparison problem remains.
- Every profile has a name following the documented convention.
- Every profile has a recorded owner and second-factor holder in your policy.
- Every profile has one proxy route, and the mapping has been reviewed this month.
See it in action

Frequently asked questions
Is profile approach comparison difficult to set up for a small team?
Start with two profiles and a short naming convention. Create one profile per account, attach one proxy route to each, enable cloud sync and invite a colleague with limited permissions. Once that small set passes an isolation check, extend the same pattern with batch launch and management.
Does MetaDesk Browser (Sidest Browser) support both Windows and macOS?
Yes. MetaDesk provides Windows and macOS clients that share the same workspace model, so profiles, cloud sync and role-based permissions behave consistently across a mixed-device team. Use the official installer for each platform and keep clients updated together.
Can teammates share a workspace without mixing account state?
Yes. Every account runs in an isolated session with separate cookies, cache, local storage and bookmarks. Team collaboration adds roles on top of that isolation, so a colleague can launch a profile without inheriting another account's saved state.
What should be written down before a rollout?
At minimum: the profile naming convention, one proxy route per profile, the owner and second-factor holder for each account, the role definitions, and the joiner and leaver steps. Six lines of documentation prevent most of the rework described in this guide.
Is there a free way to try profile approach comparison?
Yes. MetaDesk offers free registration, so you can build a small workspace with a couple of real accounts and test isolation, cloud sync, batch launch and permissions before making any commitment. Confirm current plan details on the official pricing page.
Do you publish performance benchmarks for competing tools?
No. Benchmarks and feature claims about other products change often and are easy to misquote. We publish an evaluation framework instead, so you can verify each criterion on the vendor's official documentation and in a short trial with your own accounts.
When does a team usually outgrow standard browser profiles?
Common triggers are shared ownership, more than a handful of accounts, the need for per-profile proxy routes, and any requirement to review who launched what. If two of those apply, evaluate a workspace model rather than adding more manual conventions.
Put this workflow into practice
One Chromium workspace, isolated profiles for every account, and a team that can actually share them.